NOAVAXIS TECHNOLOGY · TECHNOLOGY INTELLIGENCE & SOLUTIONS
Technology changes. We explain what matters and help you act.
Practical intelligence on Microsoft 365, cloud, security, AI and automation—focused on the changes, risks and operational decisions that affect real businesses.
WHAT NOAVAXIS DOES
From technology change to practical action.
We help organizations identify Microsoft cloud risks and inefficiencies, fix the underlying problem, manage the environment and automate repetitive work.
Risk & Efficiency Review
Identify security gaps, unnecessary risk, configuration issues and operational inefficiency.
Remediation & Microsoft 365
Turn findings into a clear remediation plan and implement the required Microsoft 365 changes.
Microsoft 365 Operations
Ongoing operational support to keep Microsoft environments secure, controlled and productive.
AI & Automation
Reduce repetitive work with practical automation and AI workflows built around business outcomes.
TECHNOLOGY INTELLIGENCE
What we track
Not every technology announcement requires action. We focus on developments that change security, operations, cost, compliance or the way teams work.
New Products & Updates
Microsoft, cloud, AI and enterprise technology changes worth understanding.
Security Alerts
Important vulnerabilities, attacks, patches and identity or cloud security developments.
Impact & Issues
Retirements, breaking changes, service issues and deadlines that may require action.
Solutions & Guides
Practical guidance for assessing, fixing and managing the resulting business problem.
LATEST ALERTS & INSIGHTS
Technology changes worth acting on.
Important Microsoft, cloud and security developments explained in practical terms: what changed, who is affected and what organizations should do next.
AI Is Changing Vulnerability Management: What Microsoft IT Teams Should Prepare For
AI is accelerating vulnerability discovery. We examine what Microsoft IT teams should consider around exposure visibility, risk-based prioritization, emergency patching, defense in depth and continuous vulnerability management.
Read the analysis →Microsoft Digital Defense Report 2026: 7 Security Priorities Microsoft 365 Organizations Should Review
Microsoft's 2026 Digital Defense Report highlights a faster-moving threat landscape. We examine seven practical priorities around identity, privilege, phishing, exposure management, non-human identities and AI security.
Read the analysis →Microsoft Storm-3168: Are Compromised Service Principals a Blind Spot in Your Azure Security?
Microsoft has documented cloud attacks involving compromised service principals, highlighting the growing security risk around workload identities, application permissions and credentials.
Read the security alert →ENTRA ID · ACTION REQUIRED
Microsoft Entra ID MemberOf Changes: What Organizations Need to Do Before November 3, 2026
Organizations using MemberOf in dynamic membership configurations should review dependencies and prepare replacement configurations before Microsoft's deadline.
Read article →SECURITY ALERT
Microsoft 365 Device Code Phishing: What Organizations Should Check After the EvilTokens Campaign
Device-code phishing can abuse legitimate Microsoft authentication flows. Organizations should review authentication usage, Conditional Access and mailbox activity.
Read article →EXCHANGE ONLINE · DEADLINE
Exchange Online EWS Changes: Is Your Cross Tenant Calendar Sharing Ready?
Microsoft's EWS retirement affects some cross-tenant Free/Busy, MailTips and Calendar Sharing configurations. Organizations should identify dependencies and plan migration.
Read article →TECHNOLOGY INTELLIGENCE · 26 SEPTEMBER 2026
Technology intelligence briefing — September 26, 2026
Important developments across Microsoft, cybersecurity, AI and enterprise technology with a focus on what changed, who may be affected and what organizations should consider next.
SECURITY ALERT · MICROSOFT 365
EvilTokens Campaign Targets Microsoft 365 Through Device-Code Phishing
Microsoft says the EvilTokens phishing-as-a-service platform facilitated campaigns that compromised more than 12,000 inboxes across over 10,000 organizations worldwide.
The attacks abuse legitimate device-code authentication to obtain tokens, access mailboxes and support business email compromise activity.
What organizations should consider
Review device-code authentication usage, Conditional Access, Safe Links and suspicious mailbox activity. Microsoft recommends blocking device-code flow wherever it is not required.
Microsoft Security research →MICROSOFT SECURITY · NEW
Microsoft Introduces ISOC in Defender for the Agentic Security Era
Microsoft has introduced the Integrated Security Operations Center (ISOC) in Microsoft Defender, bringing SIEM, threat protection, threat intelligence, automation and AI capabilities closer together.
The direction reflects a broader shift toward security operations where human analysts and AI agents work from shared signals, context and controls.
Why it matters
Security teams evaluating AI-assisted operations should understand how agentic capabilities affect investigation, automation, governance and security architecture.
Microsoft announcement →THREAT INTELLIGENCE · RANSOMWARE
Microsoft Tracks Storm-2570 Across Multiple Ransomware Operations
Microsoft Threat Intelligence says Storm-2570 has used consistent post-compromise techniques while operating across multiple ransomware ecosystems, including Qilin, DragonForce, Anubis and BERT.
Observed activity includes remote-management tools, credential theft, lateral movement, attempts to weaken security controls and cloud-based data exfiltration.
Defensive priority
Organizations should monitor suspicious remote-management tooling, protect privileged credentials, restrict lateral movement and enable tamper protection.
Microsoft Threat Intelligence →ARTIFICIAL INTELLIGENCE · NEW MODELS
OpenAI Releases GPT-6 Sol and GPT-6 Luna
OpenAI released GPT-6 Sol and GPT-6 Luna on September 22 through the Responses and Chat Completions APIs.
Both reasoning models support text and image input. GPT-6 Luna is positioned at a substantially lower API cost, while GPT-6 Sol provides a higher-capability option.
Business impact
Lower model costs can make higher-volume AI automation, document processing, analysis and agent workflows practical for a wider range of organizations.
OpenAI API changelog →FEATURED GUIDE
Microsoft 365 Security Assessment: What Businesses Should Check in 2026
A structured look at Entra ID, MFA, Conditional Access, privileged access, Secure Score, Defender, collaboration security and endpoint controls.
Read the article →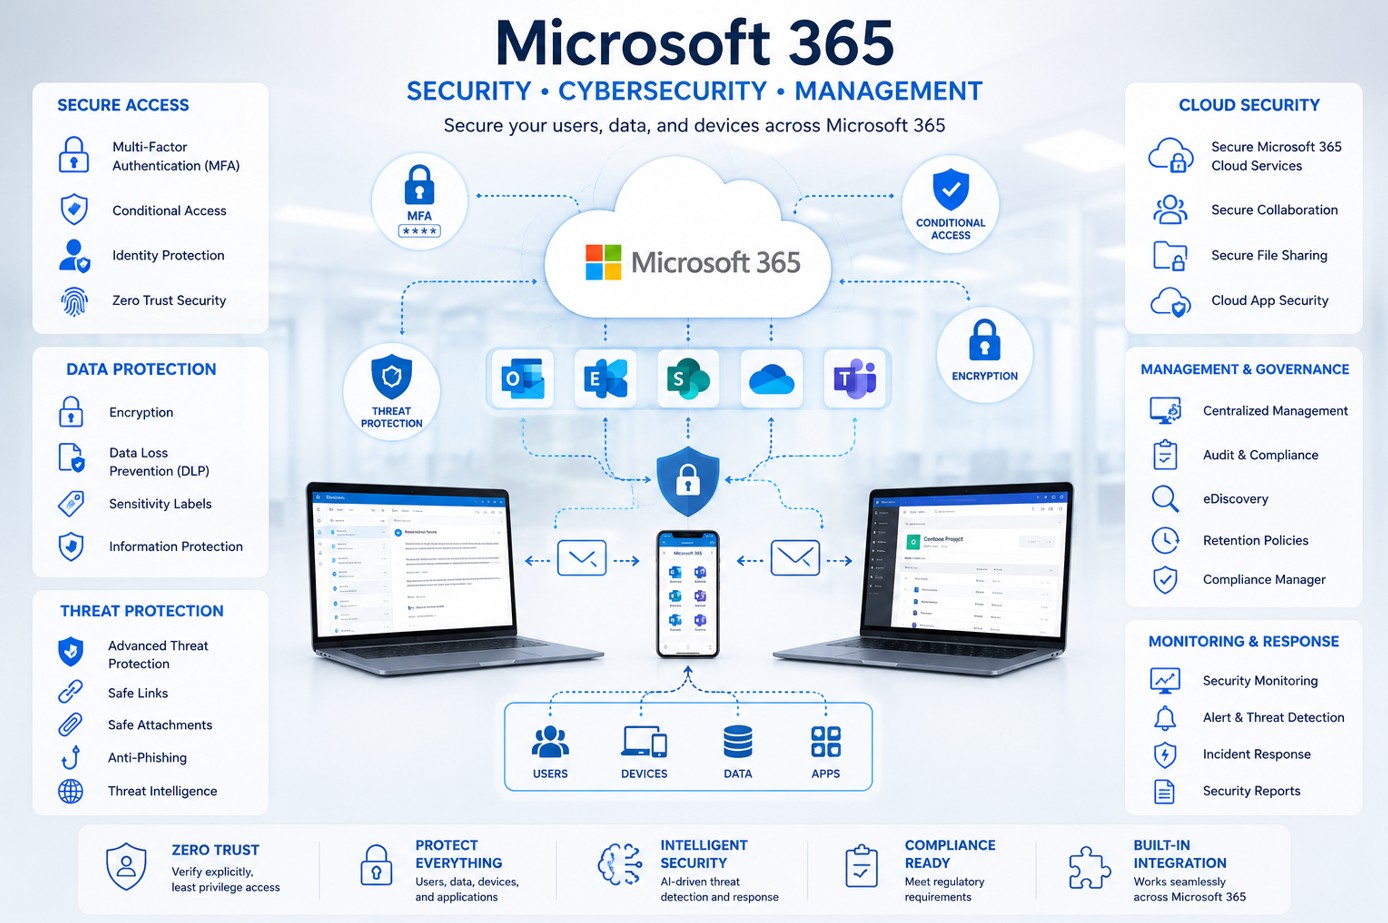
SOLUTIONS & GUIDES
Practical Microsoft 365 guidance
COPILOT
Microsoft 365 Copilot Readiness Checklist for 2026
Identity, permissions, data governance, security, licensing and adoption considerations.
Read guide →MIGRATION
Microsoft 365 Migration Planning Checklist for 2026
Discovery, identity, licensing, Exchange Online, SharePoint, OneDrive and testing.
Read guide →INTUNE
Microsoft Intune Security & Device Management Best Practices
Enrollment, compliance, Conditional Access, applications and endpoint governance.
Read guide →ENTRA ID
Conditional Access Best Practices for Microsoft 365
MFA, administrator protection, emergency access, testing and policy governance.
Read guide →MICROSOFT 365 SECURITY · ENTRA ID
Device Code Flow: A Practical Conditional Access Strategy
Learn how to identify Device Code Flow usage, reduce phishing exposure with Conditional Access, handle legitimate Teams Rooms and Teams Phone requirements, and manage exceptions safely.
Read guide →MICROSOFT 365 SECURITY RESOURCES
Practical tools for strengthening Microsoft 365 security.
Start with a practical hardening checklist or use the full assessment toolkit to review, score, document and track Microsoft 365 security improvements.
START HERE · $12
Microsoft 365 Security Hardening Checklist
A practical security-hardening baseline covering identity and access, MFA, Conditional Access, email protection, data sharing, privileged access and ongoing security maintenance.
Get the Checklist →DEEPER ASSESSMENT · $49
Microsoft 365 Security Assessment Toolkit
A structured 61-point assessment with automated scoring, evidence tracking, remediation planning, executive reporting and operational security templates.
View the Toolkit →OUR EDITORIAL APPROACH
How we approach technology intelligence
NOAVAXIS TECHNOLOGY focuses on developments that have a practical impact on Microsoft 365, cloud operations and cybersecurity.
Our approach is to reference official vendor announcements and technical documentation, explain who may be affected, and distinguish confirmed changes from operational recommendations.
Technical guidance should be checked against current product documentation before implementation, particularly where licensing, security settings or service behavior may differ between environments.
HOW NOAVAXIS CAN HELP
Concerned about an update or security issue?
We can help determine whether your Microsoft environment is affected, identify the risk and provide a clear path to remediation.
Talk to NOAVAXIS